Claude
 Cursor
 Codex
 Hugging Face
 NVIDIA
 Visual Studio Code
 Devin
 Kiro
 Open Code
 NanoClaw

 Docker
 npm
 PyPy
 Wiz

 金融サービス
 ゲーム・エンタメ
 公共部門
 自動車
 テクノロジー
 ヘルスケア


Deliver Mission-Ready, Trusted Software Supply Chain Security at Speed
Ship trusted releases at mission speed, with audit evidence built in. The JFrog software supply chain platform includes AI governance that moves teams from passive visibility to active enforcement.
Capabilities Engineered for the Mission
Built for the Environments Your Mission Actually Runs In
The JFrog Platform deploys self-hosted in your own data center or inside a fully air-gapped enclave. Govern binaries and AI assets under Policy-as-Code controls whether you’re connected or not, and extend delivery to the tactical edge.
- Deploy self-hosted, on-premises, or fully air-gapped
- Govern binaries and AI assets in one source of record inside the enclave
- Enforce Policy-as-Code gates on disconnected networks
- Extend delivery from the enclave to the tactical edge
Ship Trusted Releases With Audit Evidence, Designed to Keep Delivery Moving
Replace passive visibility with active enforcement. Releases are verified and cryptographically signed before they’re promoted, so trust is built into delivery from keyboard to warfighter, for your software and your AI assets alike.
- Promote verified software with signed release bundles
- Help block non-compliant code and unvetted AI assets with immutable policy gates
- Attach signed evidence to releases to support audit readiness
- Ship releases with audit evidence at mission speed
Act on Emergency Directives Faster
When an emergency directive hits, help gate vulnerable binaries out of your pipeline quickly. Support your continuous Authority to Operate (cATO) program with automated gating designed to reduce release delays and manual triage
- Respond across your pipelines to to CISA emergency directives in minutes
- Support cATO with automated gating
- Help block unvetted AI assets before deployment
- Apply zero-trust principles to policy enforcement across your pipelines
Move Trusted Software From Connected to Air-Gapped Environments to the Edge
Automate secure promotion from connected development to air-gapped networks, toward the warfighter. Signed release bundles carry cryptographic verification across network boundaries, designed to reduce manual re-inspection.
- Promote verified releases from low side to high side across connected to air-gapped environments
- Verify releases as single, atomic units at network boundaries
- Push verified updates to end-point devices at the tactical edge
Enforce Federal Requirements Across Your Pipeline and AI Assets
Define mission-specific rules once and enforce them across your pipelines. Reduce reliance on fragile scripts and manual evidence gathering with centralized Policy-as-Code that governs software and AI assets at scale.
- Manage mission-specific risk with less technical debt
- Reduce manual compliance paperwork for developers
- Automate evidence collection to support NIST SSDF practices and OMB M-26-05 reviews
- Free DevOps teams to move at the speed of agentic delivery
Find Threats Hidden in the Binaries You Deploy
Analyze the binaries you deploy to help expose hardcoded secrets and embedded malicious code inside proprietary software, opaque AI assets, and legacy systems.
- Help expose hidden threats in commercial and legacy software
- Help secure opaque AI assets against model-embedded malware
- Generate SBOMs from the binaries you build and deploy
- Create tamper-evident, cryptographically-signed audit trails
Support AI Executive Order Priorities Across Your Software Supply Chain
The Executive Order calls for an AI cybersecurity clearinghouse to coordinate vulnerability response, a voluntary framework for secure frontier model deployment, and 30-day directives to prioritize cyber defense of federal systems.
JFrog delivers automated AI governance, software supply chain controls, and cryptographic evidence that can help agencies support these priorities while keeping the mission moving.
AI Cybersecurity Clearinghouse (GOLD EAGLE)
Coordinate and deconflict vulnerability scanning, validation, and patch prioritization with the AI industry and critical infrastructure operators.
Automated Open-Source Remediation
Proactive vulnerability scanning and validation, with Zero-Touch Remediation that automatically replaces vulnerable Maven and npm package versions with verified patches versions.
JFrog Xray · JFrog Curation · Zero-Touch Remediation
Secure Frontier Model Deployment
Establish a voluntary framework for government evaluation of covered frontier models before release.
Secure AI Adoption
Centralized discovery and governance of AI assets, with pre-release gating designed to block unvetted AI for safer commercial and open-source adoption.
JFrog AI Security · JFrog Artifactory
Hardening Federal Information Systems
Prioritize cyber defense of national security, Department of War, and civilian and military federal systems under directives due within 30 days.
Hardened Delivery to Air-Gap and Edge
Support hardening of civilian and military federal systems through pre-distribution scanning and verified delivery to air-gapped and edge environments.
JFrog Distribution · JFrog Artifactory
Compliance
Enforce pre-mapped NIST SSDF practices as Policy-as-Code, with less manual policy writing. Signed evidence and real-time coverage scoring help keep binaries and AI assets ready for attestation and ATO reviews.

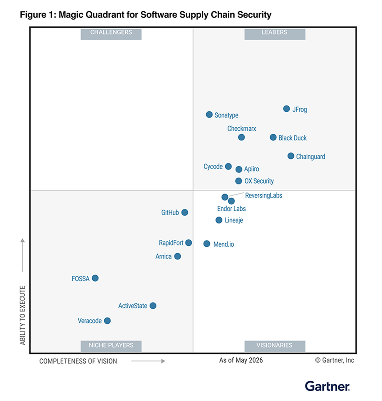
JFrog named a Leader in the 2026 Gartner® Magic Quadrant™ Software Supply Chain Security
Highest in Ability to Execute. Recognized for Strengths in Innovation, Offering (Product) Strategy and Operations.
Beyond Federal: JFrog for SLED and Non-Profit Organizations
Power Public Services with Trusted Software Supply Chain Security
JFrog delivers enterprise-grade governance scaled to your mission for state agencies, city and county governments, school districts, and universities facing the same software supply chain threats and AI governance challenges as federal agencies.
- Support state-level cybersecurity requirements with automated policy enforcement
- Help reduce supply chain risk to applications and AI assets that handle student and citizen data
- Generate SBOMs and compliance evidence you can use for audits, with less manual paperwork
- Deploy across on-premise, self-hosted, and disconnected campus environments
Enterprise Security for Mission-Driven Software
JFrog gives mission-driven organizations enterprise-grade software supply chain security and AI governance without enterprise complexity.
- Manage binaries and AI assets in one secure source of record
- Help block malicious open-source packages before they reach development
- Generate evidence you can use for funder, board, and regulatory reviews
- Scale software delivery without scaling security overhead
Additional Resources
Automating Federal Software Supply Chain Compliance
JFrog Software State of the Union Report and the AI Executive Order 14409
Active AI Risk Elimination in the Federal Software Supply Chain
Importance of Securing the Software Supply Chain
Frequently Asked Questions
Yes. The JFrog Platform deploys self-hosted, on-premises, or fully air-gapped, with Signed Release Bundles carrying cryptographic trust across disconnected networks.
JFrog is available through established federal contract vehicles and works with systems integrators supporting civilian, defense, and intelligence community missions.
JFrog governs AI models, agent skills, and AI-generated artifacts alongside your software binaries, scanning for embedded malware and enforcing policy before anything reaches production.
JFrog automates evidence collection, SBOM generation, and provenance aligned to NIST SP 800-218 (SSDF), NIST SP 800-53, Executive Order 14028, OMB M-26-05, and the June 2026 AI Executive Order (EO 14409). Cryptographically signed Lifecycle Evidence at every SDLC gate supports continuous Authority to Operate (cATO) and satisfies FISMA and DoD authorization reviews without manual paperwork.
JFrog automates secure promotion from unclassified development environments to classified networks. Every release is packaged as a signed bundle that carries cryptographic proof of its contents and origin across each network boundary, so it can be verified on the high side without manual inspection or re-scanning. Agencies can also run a hybrid model, developing on the low side and promoting verified releases to self-hosted instances on the high side.
Connect with a JFrog Public Sector Expert
Connect with specialists who understand your mission and help public sector organizations support their work under EO 14409, NIST SP 800-218, and, for federal civilian agencies, CISA BOD 26-04. Request a demo to see how JFrog helps keep mission-critical software secure and ready to deploy and supports your compliance work.