Claude
 Cursor
 Codex
 Hugging Face
 NVIDIA
 Visual Studio Code
 Devin
 Kiro
 Open Code
 NanoClaw

 Docker
 npm
 PyPy
 Wiz

 Financial Services
 Gaming
 Public Sector
 Automotive
 Technology
 Healthcare


JFrog Names Nine Global Winners for Inaugural Software Supply Chain Excellence Awards
Organizational excellence recognized at swampUP 2026 demonstrating that trust can be engineered into the software supply chain at scale
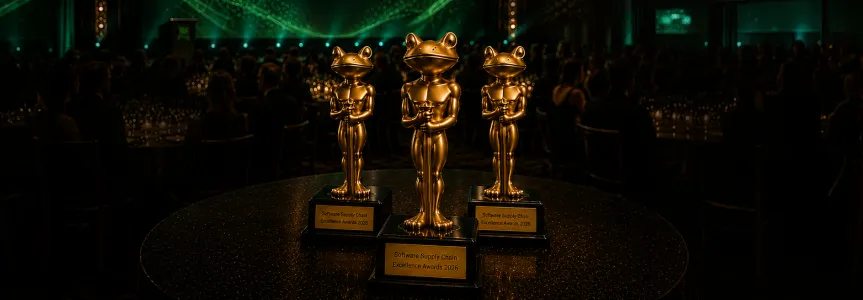
JFrog announced completion of the first-ever Software Supply Chain Excellence Awards, recognizing the teams who have turned their software supply chain into a competitive advantage – unifying development, security and operations around a governed, automated ecosystem that delivers trusted software at scale.
The nine honorees span the Americas, Europe, and Asia-Pacific, across three categories: Unified Platform, Trusted AI Adoption, and Software Supply Chain Security.
“Agents now write, review and deploy code faster than ever, while malicious AI models, agent skills and extensions are turning up in the registries developers use daily. Increasing regulations require proof at every step – from code to runtime,” said Roie Shorer, Chief Growth Officer at JFrog. “The companies that pull ahead in the AI era will be those going beyond simply automating for speed and scale. They will be the ones who can see exactly what’s shipping and why, as they bring trust, control and adaptability to their development operations. This year’s winners didn’t just add tools; they established a single source of truth where developers, security, and compliance teams can operate using the same data and the same rules. We’re very proud of all of them and thrilled to be part of their journey.”
Software supply chains are being put under new strain as developer teams grapple with AI-era software challenges. In its 2026 Software Supply Chain Security report, JFrog identified over 900 malicious AI agent skills carrying high-impact payloads alongside 495 malicious AI models on Hugging Face and 56 malicious extensions on OpenVSX. Attackers are no longer just targeting code; they are targeting the autonomous tools that write, review, and deploy it.
This year’s JFrog Software Supply Chain Excellence Award winners are working to reduce their exposure to these emerging threats by building a system of record that governs and secures artifacts from end-to-end – mastering the AI surge with speed and trust.
THE CONVERGENCE AWARD
The Convergence Award recognizes teams that unify a fragmented software delivery workflow – bringing previously disconnected repositories, scanners and tools into a single governed system of record.
Here are the winners:
Ford (Americas): Ford Motor Company has more than 15,000 developers spread across 80-plus global plants, which previously ran on separate repository tools and scanners with no shared visibility between them. By consolidating operations into a unified ecosystem with the JFrog Platform, Ford reduced tool sprawl and turned multiple blind spots into a single pane of glass view for IT and security teams. As a result, the team now manages more than 43 million artifacts on the JFrog Platform with 99.99% uptime. The team credits the consolidation with recapturing an estimated $8 million a year in developer productivity.
SCHOTTEL Industries (EMEA): Schottel replaced fragmented artifact storage and open-source consumption with the JFrog Platform. Over six months it delivered more than 32,000 artifacts, curated over 2,300 open-source packages and automatically blocked more than 900 risky ones. Manual dependency approval processes that previously delayed developers by months were replaced by automated governance and security controls, enabling faster adoption of new technologies while helping maintain its compliance and security standards.
Rakuten Symphony (APAC): Rakuten Symphony runs 28 self-hosted JFrog Enterprise+ instances across India, Japan and Singapore, that are all connected by JFrog Federated Repositories into one collaborative environment. With JFrog Curation and JFrog Advanced Security moving controls to the point of ingestion, the company cut manual triage efforts by roughly 60% in a single month across more than 600 releases, reclaiming more than 500 engineer-hours and pre-triaging over half of its vulnerability workload automatically.
THE TRUSTED INTELLIGENCE AWARD
The Trusted Intelligence Award recognizes teams that bring enterprise-grade governance to AI and model lifecycles, helping trust extend far beyond just supporting application code.
Here are the winners:
NVIDIA (Americas): Models repositories are under enterprise identity control, with a shared curation and scanning policy,which means a downloaded model faces the same checks as a package before it reaches production.
NVIDIA brought its AI model distribution surface under a governed perimeter by applying curation, scanning, and policy enforcement directly to its model mirrors. Thousands of AI model seats are now managed inside a controlled, auditable boundary, transforming what was once an unmanaged distribution surface into a demonstration of DevGovOps operating at true enterprise scale. To get there, NVIDIA leveraged JFrog Curation and JFrog’s scanning and policy tools, piloting them on the infrastructure through which its AI models flow.
Husqvarna Group (EMEA): Husqvarna’s autonomous divisions, across forest, garden and construction equipment, had accumulated overlapping scanners with limited shared visibility into software supply chain risk. After consolidating around the JFrog Platform and introducing software package scanning and policy-based controls earlier in the software development lifecycle, builds were progressively onboarded, providing teams with greater visibility into open-source dependencies and a more consistent approach to software component governance. Husqvarna Group validated JFrog Curation and JFrog Advanced Security in a hands-on pilot ahead of full deployment, and says the centralized visibility helps streamline security and governance workflows while supporting software traceability and reporting needs associated with evolving regulatory requirements, including the EU Cyber Resilience Act and NIS2.
Singapore Airlines (APAC): Singapore Airlines moved from “trust by verification” to “trust by default.” JFrog Curation and JFrog Xray now help intercept malicious, risky or non-compliant assets before they reach a build, including AI models, MCP servers, agent skills and IDE extensions. More than 95% of AI and open-source dependencies are onboarded through curated channels prior to integration. As a result, late-stage release blocks from non-compliant dependencies are down 60-75% and the airline has full visibility of its compliance posture.
THE GUARDIAN AWARD
The Guardian Award recognizes software supply chain security operating at real enterprise scale – blocking threats before they reach production across large, highly distributed environments.
Here are the winners:
S&P Global (Americas): S&P Global’s five divisions ran on independent JFrog Artifactory clusters with no shared policy enforcement which could potentially increase risk. By putting JFrog Curation at each point of ingestion – backed by continuous rescanning – S&P addressed that gap without slowing down development teams. Critical vulnerabilities across 30 images fell by 90%, from 141 to 14. S&P reports that about 99% of malicious npm and PyPI packages are now blocked at the point of ingestion, with JFrog Curation deployed as a synchronous gate for every division and JFrog Xray continuously rescanning artifacts already in use to catch newly disclosed threats.
TSB Bank (EMEA): TSB built a continuous governance platform based on JFrog’s APIs, using GitHub Actions and Open Policy Agent, as well as a versioned Python library published to JFrog Artifactory. Automated weekly audits check configuration drift, access control, artifact integrity and artifact authenticity. In the first seven months of using the platform there were 75 governance issues, 74 of which were resolved, with 11 production repositories verified for integrity every week.
Iress (APAC): Iress put the SaaS implementation of JFrog Artifactory at the center of their 600 developer operations, and added JFrog Curation and JFrog Xray to help keep zero-day threats from entering the development environment. In just eight months, the curation initiative mitigated six critical security incidents, while eliminating 90% of reactive vulnerability triage – saving the team an estimated 13,705 engineering hours for the year.
THE SELECTION PROCESS
Award winners were selected by a cross-functional panel of JFrog leaders and industry voices who scored each submission on the breadth of its story and the strength of its metrics. The complete list of winners and full category criteria are available at jfrog.com/software-supply-chain-awards.
You don’t have to be an award winner to experience the advantages of the JFrog Platform. Schedule a demo today and perhaps your team will be joining us on the podium next year.
Important Notice: This blog post is provided for general informational purposes only. It reflects information available as of the publish date shown at the top of this blog post, and JFrog may not update it. It is provided “as is,” without warranty of any kind, is not legal, compliance, or security advice, and does not guarantee any security, product, financial, or legal outcome. To the extent permitted by law, JFrog is not liable for any decision made or action taken in reliance on it. Third-party statistics and studies are reported as published by their sources and have not been independently verified by JFrog. JFrog does not author or warrant third-party AI assets listed in or governed through its products. Results depend on your environment, situation, and configuration. Product capabilities vary by edition and deployment model. Nothing in this blog post creates any commitment or modifies any agreement. Your use of JFrog products is governed by your agreement with JFrog. JFrog is a registered trademark of JFrog Ltd. in the United States. All other trademarks referenced in this document are the property of their respective owners, and their use does not imply any affiliation with or endorsement by them.
Experience
JFrog Today
Discover how the JFrog Platform unites DevOps, DevSecOps and MLOps for secure, rapid software delivery.