


 Claude
 Cursor
 Codex
 Hugging Face
 NVIDIA
 Visual Studio Code
 Devin
 Kiro
 Open Code
 NanoClaw

 Docker
 npm
 PyPy
 Wiz

 Financial Services
 Gaming
 Public Sector
 Automotive
 Technology
 Healthcare


Enforce your policies. Every agent. Every pull.
Detect and secure AI assets across your agentic software supply chain, so your agents consume only approved ones.
What is JFrog AI Security?
JFrog AI Security controls how coding agents and developers use AI assets. It detects agent skills, plugins, MCP servers, and models, scans them for risk, and blocks anything you have not approved.
JFrog AI Security is the new name for JFrog AI Catalog.

Discover Pre-Approved
AI Assets
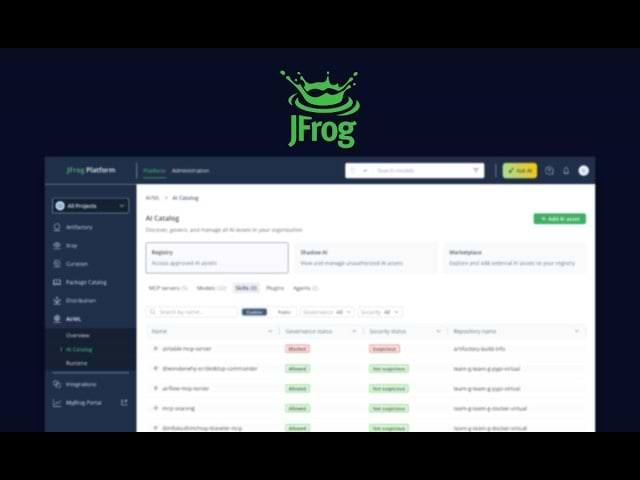
One registry for every AI asset, stored as native artifacts in Artifactory alongside your other binaries. Coding agents and developers discover and self-serve pre-approved assets from one source of truth: immutable, versioned, and traceable back to the release they shipped in.
Detect Shadow AI on Developer Machines
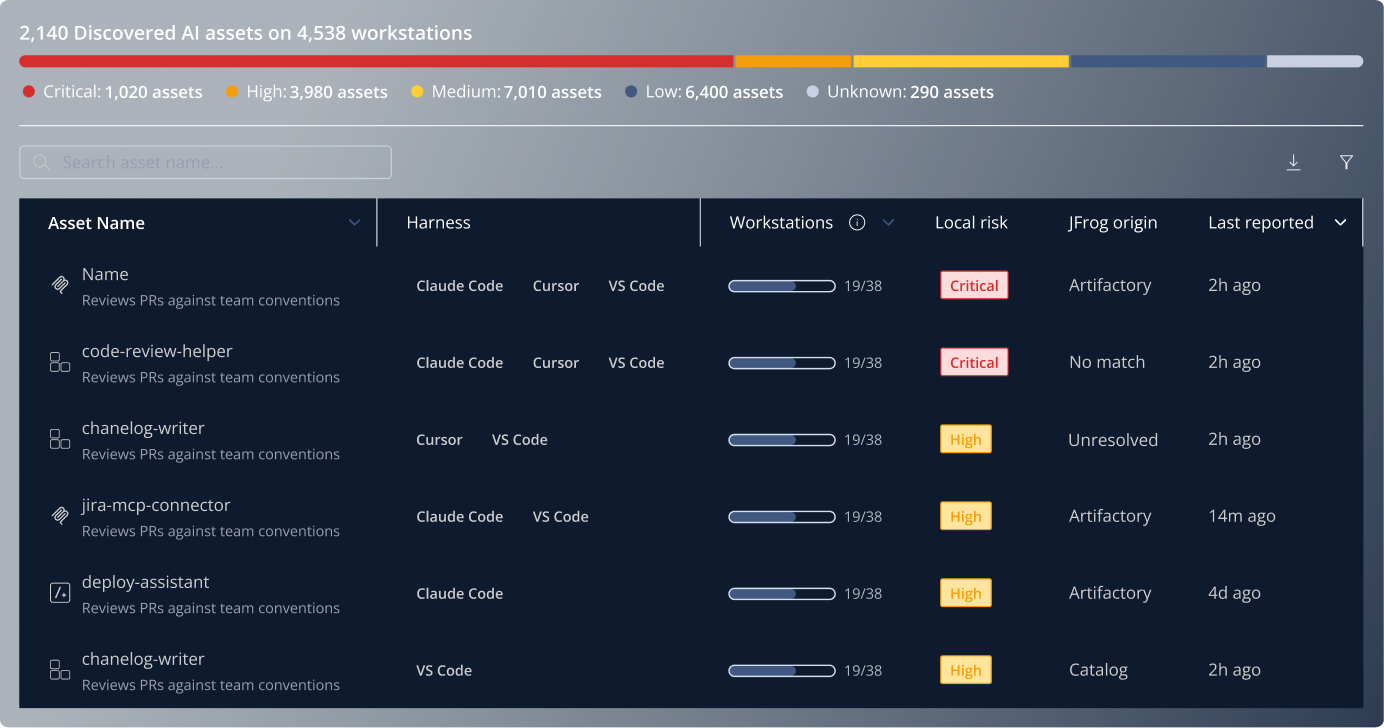
Expose what your coding agents actually run on developer machines: skills, MCP servers, and plugins. Spot the risky ones, see how many workstations run each, and tell which are managed in JFrog and which aren’t.
Scan and Detect Shadow AI in Your Software Supply Chain
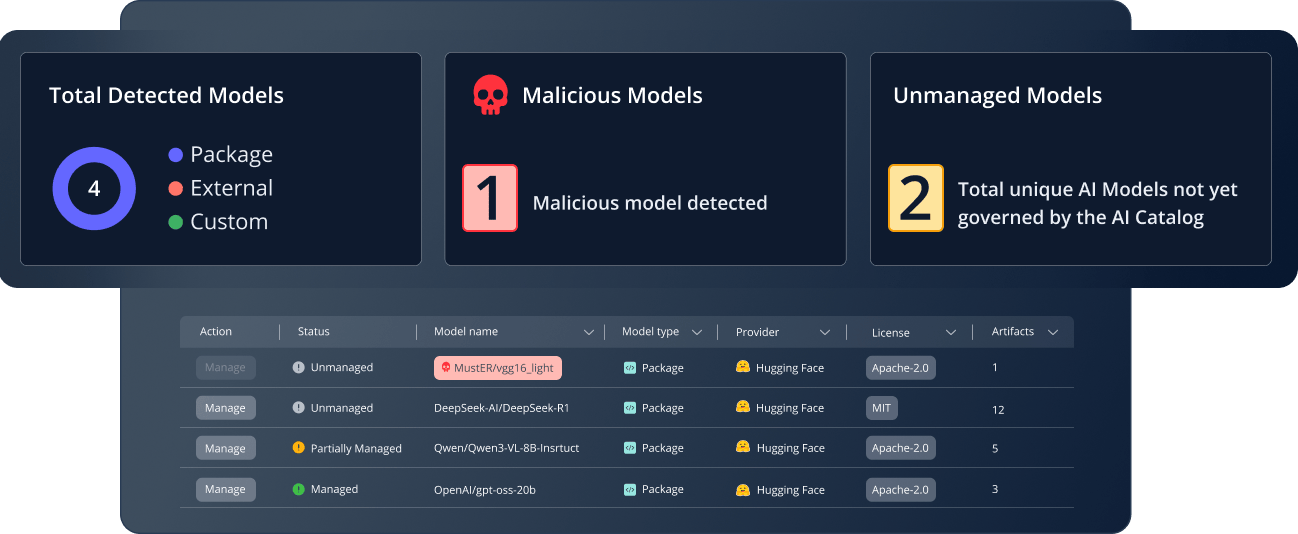
Scan your software supply chain to expose the models and calls to external AI services in use, including the ones pulled without approval. See what's managed, unmanaged, or malicious at a glance, and govern or block it on the spot.
Block Risky AI Assets Before They’re Pulled
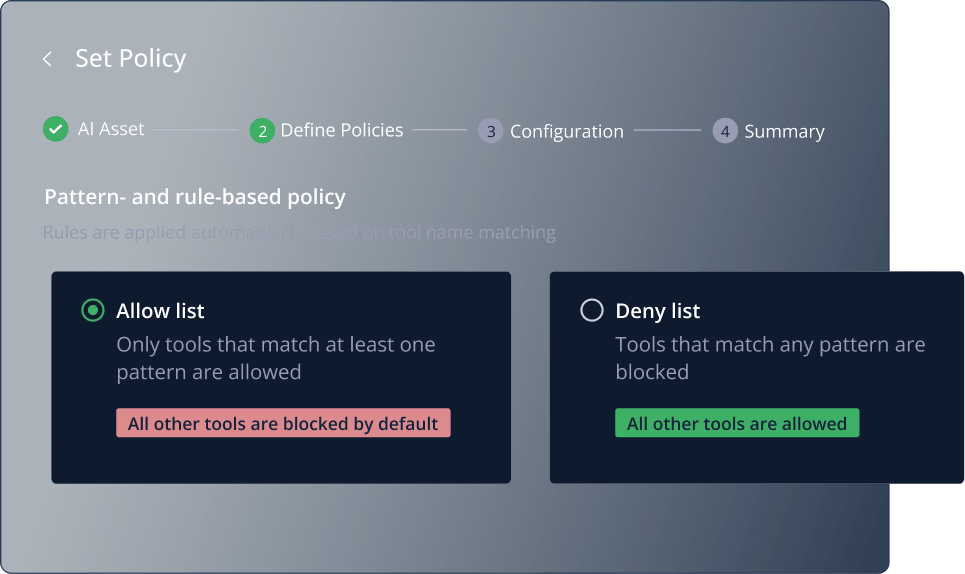
Stop unvetted or non-compliant AI assets at the gate before they ever reach your software supply chain. The same Curation control enforces your policies on models, MCPs, plugins, and skills.
Scan AI assets for Risk
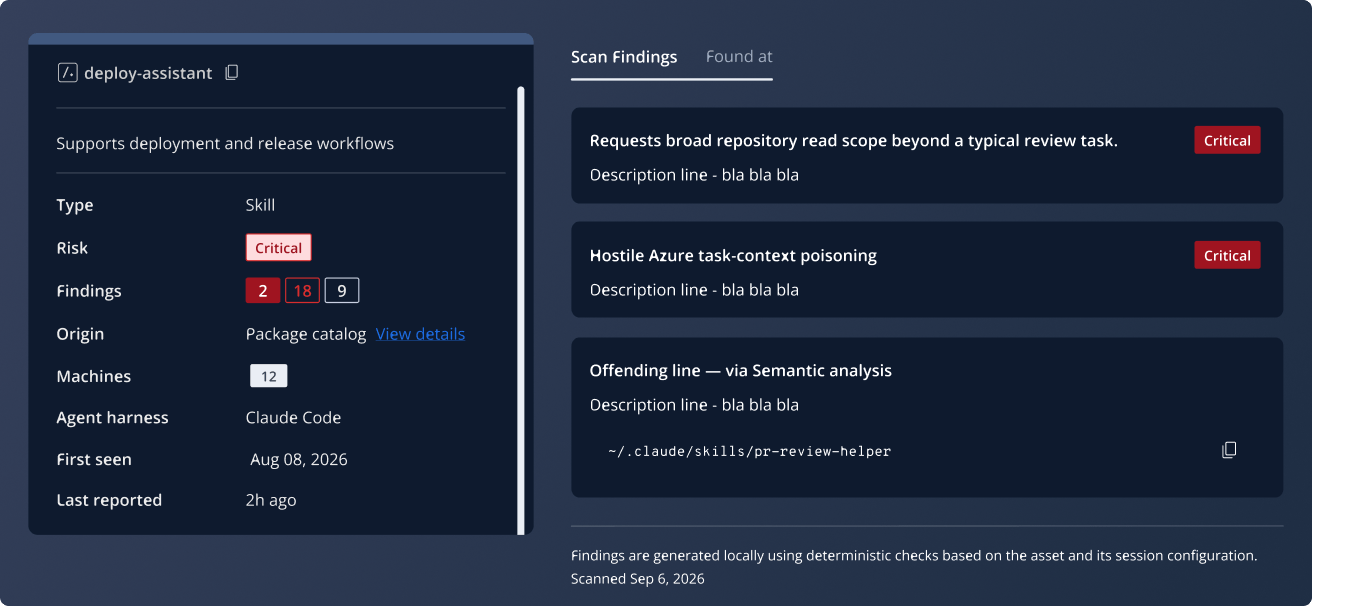
Continuously evaluate what each agent skill, plugin and APM instructs an agent to do. Combine deterministic and semantic scanning to catch suspicious or malicious intent hidden in plain text, using JFrog's model or your own LLM key.
Enforce Approved AI Assets with Agent Guard
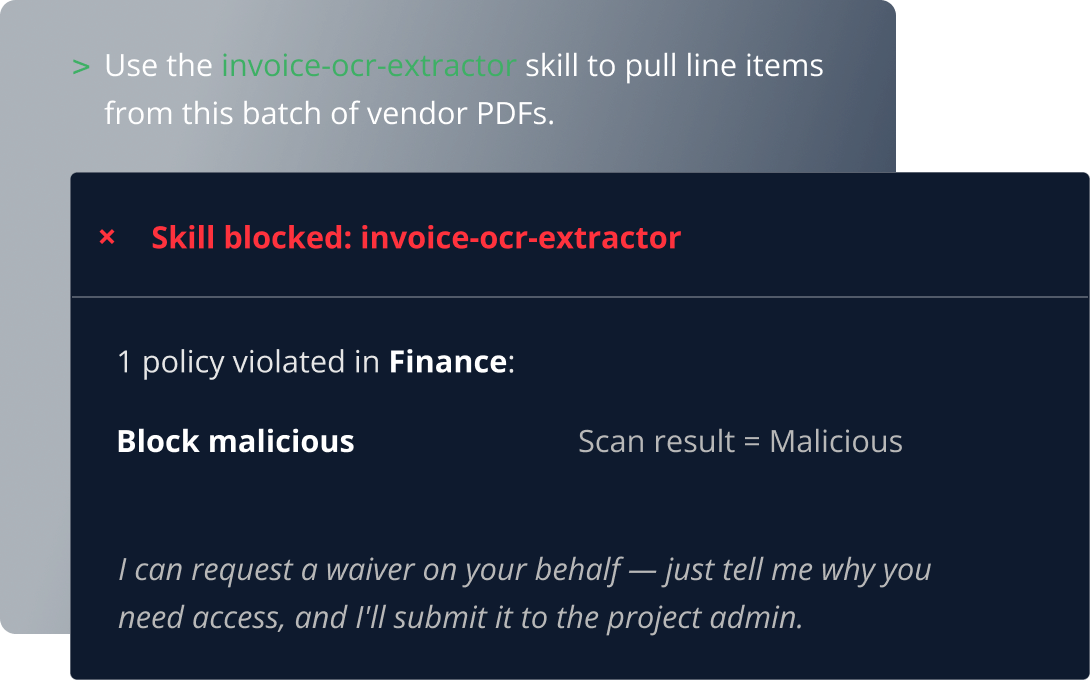
Your coding agents reach only the assets you've approved, so autonomous development stays fast and on-policy. Agent Guard routes every coding agent (Cursor, Claude Code, Codex, etc.) through an authenticated bridge that validates each request against your rules.
Agentic Velocity
Doesn’t Mean Losing Control
Doesn’t Mean Losing Control
JFrog AI Security blocks unapproved AI assets at the agent harness, so teams can ship quickly and stay in control.
Additional Resources
Frequently asked questions
-
A universal AI Registry is a single source of truth for every AI asset an organization uses (models, MCP servers, agent skills, plugins, and APM) so teams can discover, evaluate, and govern them all in one place. Enterprises need one because developers and coding agents now pull these assets directly from public sources onto laptops and into builds, without approval or review. That creates Shadow AI that security teams can’t see or control. An AI Registry closes the gap by treating AI assets like any other software artifact: versioned, scanned, access-controlled, and auditable, thus improving enterprise AI governance.
-
JFrog AI Security detects Shadow AI in two places. In your software supply chain, it exposes the AI models and calls to external AI services in your repositories and builds, including the ones pulled without approval. On developer machines, it exposes the skills, MCP servers, plugins, hooks, commands, and monitors your coding agents run, including how many workstations run each, their local risk, and whether it’s managed in JFrog. The result is a baseline of the AI actually in use, so you can decide what to approve and enforce with Agent Guard.
-
JFrog blocks risky AI assets at the point of request, before they ever enter your environment, using JFrog Curation as a preventive gate. When a developer or coding agent requests a model or MCP server, JFrog checks it against your policies and physically stops any asset that’s vulnerable, malicious, or unapproved, the same way JFrog gates npm packages and Docker images.
-
JFrog AI Security uses Agent Guard that authenticates every tool call or skill usage a coding agent makes and enforces granular, role-based access control. Agents like Cursor and Claude Code can only reach pre-vetted, approved AI assets. Instead of banning agents or granting blanket approvals, you define exactly which assets and actions each agent is allowed, and the Agent Guard enforces it.
-
JFrog AI Security integrates with leading AI coding agents and IDEs via the official JFrog agent plugins, including Cursor, Claude Code, GitHub Copilot, OpenAI Codex, Kiro, IntelliJ, Devin, VS Code, and OpenCode.
-
JFrog AI Security detects agent skills, plugins, and MCP servers on developer machines, and models and calls to external AI services in your software supply chain. It scans agent skills and plugins with deterministic and semantic scanning as they enter Artifactory, and checks the assets it finds on developer machines for local risk. It controls agent skills, plugins, and MCP servers through Agent Guard, so coding agents use only the ones you approved.



