A private Docker registry catalogues a collection of Docker repositories, while limiting access. Each repository holds container images that can be distributed to a Docker engine. Docker registries can be accessed through the Docker client, or through the Docker Registry HTTP API, to push images to, or distribute images from the repositories in its collection.
Privacy protection
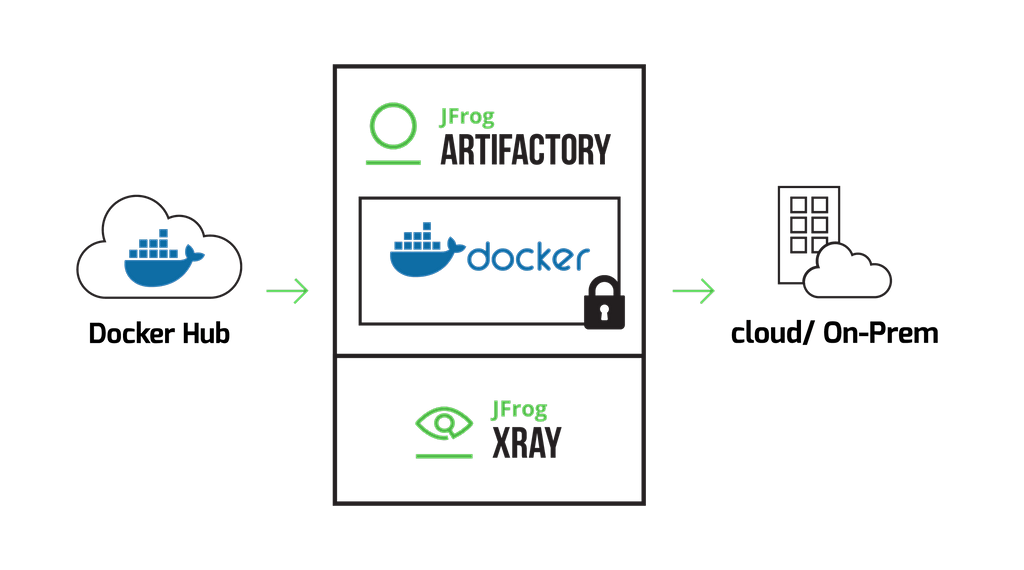
A private Docker registry in Artifactory securely shares collections of Docker repositories within your organization, limiting use to those with permissions. When installed on-premises in your data center, Artifactory can maintain your Docker trusted registry on your own server, behind your organization’s firewall along with all of the sensitive data you need to protect for security or regulatory compliance.
Fully compatible with Docker
Artifactory supports the relevant calls of the Docker Registry HTTP API, so you can manage all your Docker images in Artifactory transparently with the Docker client. Just invoke Docker from the command line as you would any other Docker registry service to add images to a repository or pull images for distribution to a Docker engine.
Control access to apps
Define multiple Docker registries in Artifactory, as many as you wish, to manage each project in its own registry. Each registry may have its own authentication credentials, so you can control fine-grained access to your Docker images and enforce isolation of applications between groups in your organization.
Flexible as you need
In any private Docker registry in Artifactory, you can mix whatever types of Docker repository held by Artifactory that you choose. So you can include Docker repositories of the containers you built yourself, as well as Docker repositories in Artifactory that proxy from remote Docker resources such as Docker Hub.


 Claude
 Cursor
 Codex
 Hugging Face
 NVIDIA
 Visual Studio Code
 Devin
 Kiro
 Open Code
 NanoClaw

 Docker
 npm
 PyPy
 Wiz

 金融サービス
 ゲーム・エンタメ
 公共部門
 自動車
 テクノロジー
 ヘルスケア